
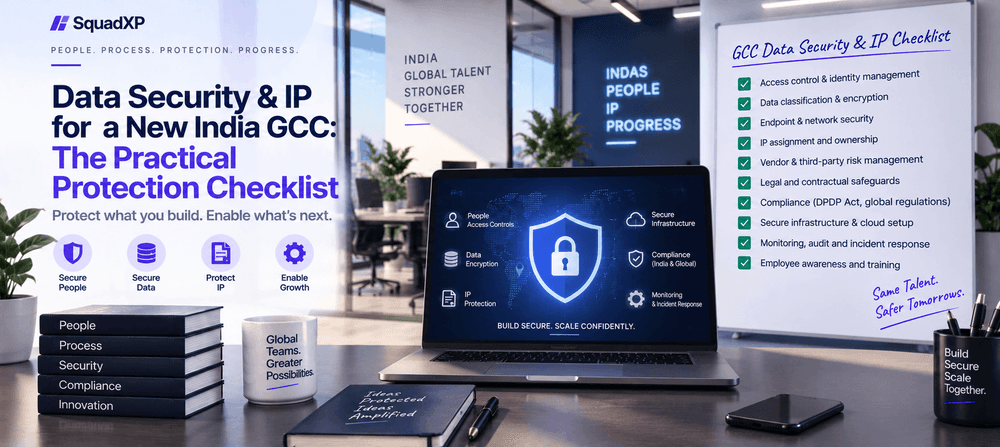
A new GCC gives a company talent, engineering capability, and potentially real product ownership. It also expands the company's security surface.
Employees may touch source code, customer information, internal systems, cloud infrastructure, product roadmaps, AI models, financial data, and intellectual property. That means data security and IP protection can't be bolted on after the team is running, they have to be part of the GCC design. SquadXP's GCC hiring content treats security, risk, and compliance as capabilities to consider early rather than retrofit, and this checklist offers a practical way to protect data and IP when you set up in India.
This is an operational and strategic guide, not legal advice. Employment agreements, IP assignment, privacy, tax, regulatory requirements, and cross-border data questions should be reviewed with qualified Indian and home-country counsel.
The biggest risks are usually basic
The most common GCC risks aren't sophisticated attacks, they're organisational gaps: excessive access, poor offboarding, unmanaged devices, weak identity controls, unclear IP ownership, uncontrolled third-party access, poor data classification, inconsistent policies, incomplete logging, and untrained employees. So a mature strategy starts with fundamentals, not exotic tooling.
Lock down IP ownership and agreements first
Before anyone joins, identify the critical assets the GCC will touch, software (source code, APIs, algorithms, architecture), product (roadmaps, designs, specs), AI (models, training data, prompts, evaluation systems), business (pricing, customer data, financial models), and corporate (strategy, contracts). You can't protect what you haven't identified. Then define IP ownership clearly: who owns employee-created work, how inventions and contractor-created assets are handled, which agreements apply, and what happens when people leave, all reviewed by counsel rather than a generic template.
Make sure employment agreements address confidentiality, IP assignment, inventions, trade secrets, data handling, acceptable use, security obligations, and post-employment obligations, and don't apply weaker standards to contractors who can reach code, data, product systems, or customer information. These IP and access decisions are inseparable from the GCC IT setup, so design them together.
Control access with classification and least privilege
Create clear data classification, public, internal, confidential, restricted, and critical, each with its own access and handling rules. Then default to least privilege: an engineer who doesn't need production access shouldn't have it, and a developer who needs a repository but not the finance system should have those permissions separated. Underpin it with identity security, SSO, MFA, strong authentication, role-based access, privileged access controls, and access reviews, since identity is the foundation of security in a distributed GCC.
The joiner, mover, leaver process is one of the most important controls: create only approved access on joining, change it when responsibilities change, and revoke it immediately on departure, automated where possible rather than relying on a manager remembering to send an email. For engineering GCCs, protect source code with repository permissions, branch protection, code review, secret scanning, audit logs, device controls, and dependency scanning, and avoid broad repository access just because "everyone is an engineer." Treat production access as privileged, using just-in-time access, approval workflows, PAM, audit logs, and break-glass procedures.
Secure the environment and plan for the worst
Manage cloud security (IAM, roles, secrets, keys, security groups, logging, segmentation) and review permissions regularly. Keep endpoints encrypted, managed, patched, monitored, and remotely manageable, and evaluate BYOD carefully for sensitive work. Apply data-loss prevention proportionate to risk, and assess third-party risk across IT providers, recruiters, cloud vendors, office providers, contractors, and managed services by asking what data each can access. Run security awareness training during onboarding and periodically, covering phishing, passwords, MFA, data classification, social engineering, device security, and incident reporting.
Build an incident-response process before the first incident, defining who detects, investigates, communicates, contains, contacts legal and customers, and reports to regulators, none of which should be invented mid-breach. Monitor identity, endpoints, cloud, network, repositories, and production systems, and give offboarding special attention: disable accounts, recover devices, revoke tokens, review privileged access, preserve logs, confirm information is returned, and complete contractual steps. Set remote-work rules for company devices, home networks, MFA, secure access, and public Wi-Fi. And because modern GCCs increasingly use AI, create an AI-use policy before employees experiment: can they paste proprietary code into AI tools, can customer data go to external models, who owns generated output, which models are approved, and how are prompts and outputs stored?
Balance security with productivity
Sequence maturity sensibly, identity, MFA, endpoint management, basic access controls, contracts, and training at launch; DLP, SIEM, PAM, automated provisioning, and vendor security at scale; zero-trust, advanced detection, continuous monitoring, and dedicated security leadership at maturity. And remember the goal isn't "block everything," it's to make the secure path the easiest path: role-based access instead of manual approvals, SSO and MFA instead of remembered password policies, endpoint management instead of manual device checks. Automation makes security more usable, and governance over who can access what ties directly into the India-to-HQ operating model.
Conclusion
Data security and IP protection shouldn't be a compliance checklist that appears after the GCC has hired 100 people, they're part of the operating architecture. The best approach is identify, classify, restrict, monitor, review, revoke. A new GCC should make it easy for people to access what they need and hard to access what they don't. That balance is what lets the center scale without turning security into either an uncontrolled risk or a productivity bottleneck.